Posts tagged "security"
18 posts tagged with security.
Argon2 vs Bcrypt vs Scrypt: Which Password Hash Should You Use?
Modern password hashing has three serious contenders. We compare Argon2, bcrypt, and scrypt on memory hardness, GPU resistance, ecosystem support, and OWASP's current recommendation.
API Keys: How They Work, Best Practices, and What to Avoid
API keys are the workhorse of server-to-server authentication, but a leaked key can mean thousands of dollars in fraudulent charges. Here's how they actually work, where to store them, and how to design rotation that survives contact with reality.
X.509 Certificates Explained: Anatomy of the Web's Identity Layer
Every HTTPS handshake, every code-signing check, every TLS-secured email rests on X.509. We dissect the fields, extensions, chain of trust, and what each section actually does.
Digital Signatures and PDF Security: How They Actually Work
A PDF digital signature is not a scanned image of your handwriting — it is a cryptographic proof tied to a certificate. Here is what it actually verifies and what it does not.
Common PDF Redaction Mistakes That Leak the Information You Tried to Hide
From the TSA 2014 manual to the Manafort 2019 filing, the most famous PDF redaction failures all happened the same way — a black rectangle drawn in a generic editor over text that was never actually removed. Here are the specific mistakes and how to verify before you ship.
How TOTP Two-Factor Authentication Works (RFC 6238)
Those six-digit codes from Google Authenticator, Authy, and 1Password are not magic. They're HMAC over a clock. Here's the precise algorithm, the security model, and why drift handling matters.
How PGP Encryption Works: Keys, Trust, and Real-World Use
PGP (and OpenPGP) has secured email and files since 1991. We explain key pairs, the web of trust, signing vs encrypting, and where PGP still makes sense in 2026.
How PDF Redaction Actually Works (And Why Black Boxes Are Not Enough)
Drawing a black rectangle over text in a PDF does not redact it. We show how proper redaction strips the underlying content stream, why metadata matters, and famous cases where it went wrong.
How Bcrypt Hashes Passwords (And Why Cost Factor Matters)
Bcrypt is the password-hashing standard most modern apps still rely on. Here's how the Blowfish-based KDF works, why the cost factor matters, and how to pick a value that ages well as hardware speeds up.
Content Security Policy (CSP): What It Stops, What It Doesn't
CSP is the most powerful XSS defense most sites either don't use or deploy wrong. Here's what it actually stops, what it doesn't, and how to ship a working policy without breaking everything.
Environment Variables and Secrets Management Best Practices
A hardcoded API key committed to a public repo is a nightmare that keeps on giving. Here is a practical guide to managing environment variables and secrets safely across environments.
How TLS and HTTPS Work: From Handshake to Encrypted Connection
Every HTTPS connection starts with a TLS handshake — a sub-second ceremony that establishes identity and agrees on encryption keys. Here is the full sequence in plain English.
Public Key Cryptography Explained Simply: Keys, Ciphers, and Signatures
The magic behind HTTPS, SSH, and PGP encryption is public key cryptography — a system where you can encrypt a message that only the intended recipient can decrypt. Here is how it works.
How OAuth 2.0 Works: Flows, Tokens, and Security in Plain English
OAuth 2.0 is the standard behind every "Sign in with Google" button — yet the underlying flow confuses many developers. This post maps out exactly what happens behind the scenes.
Understanding CORS: Why It Exists and How to Actually Fix It
CORS errors block your frontend from talking to your own API — and the fix is not to disable it. Understanding why browsers enforce the same-origin policy makes the solution obvious.
Hashing Algorithms Explained: MD5, SHA-256, bcrypt — When to Use Which
MD5 and bcrypt are both called hashing algorithms, but they serve completely different purposes. This guide explains what makes a hash function suitable for checksums versus password storage.
Encoding vs Encryption vs Hashing: The Key Differences Explained
Treating Base64 as encryption or MD5 as a secure hash are among the most common security mistakes developers make. This post draws a clear line between encoding, encryption, and hashing.
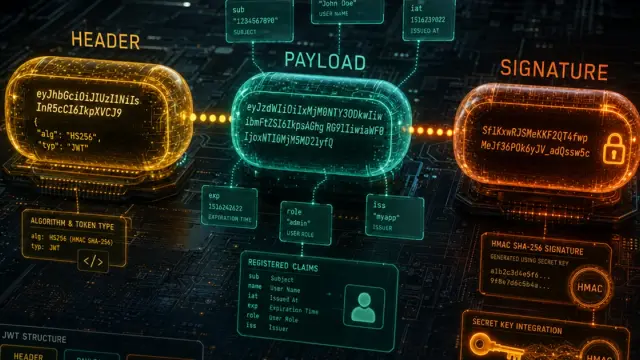
JWT Tokens Explained: Structure, Security, and Common Pitfalls
A JWT looks like random text until you decode it — then you find a header, a payload, and a signature. This post explains exactly what each part does and why that matters for security.